Start with what is going wrong
Responses chased through email, the same evidence requested by several teams, overdue reviews that are hard to track. These point to the capabilities that matter, and the ones you can ignore.
Software · TPRM · Banking in Asia
Picking the best TPRM software for your bank takes more than meeting functional requirements. In Asia especially, the considerations you overlook can stall your project.
Last reviewed: October 2026
Key takeaway
The best TPRM software for a bank in Asia depends on more than features, and other constraints are easily missed, such as where the software can be hosted, whether support covers your business hours and whether the portal works in the languages your existing service providers use. These constraints grow when many software suppliers have limited offices in Asia. This page sets out the key considerations, so your team avoids shortlisting suppliers it may have to drop at a later stage.
The best third-party risk management (TPRM) software for your bank, sometimes sold as vendor risk management software, is the one that supports the oversight work you need to improve: onboarding third parties, collecting evidence, completing assessments, monitoring changes and following up on findings. The same considerations apply to insurers, asset managers and other financial institutions operating across Asia.
Responses chased through email, the same evidence requested by several teams, overdue reviews that are hard to track. These point to the capabilities that matter, and the ones you can ignore.
Reuse a provider's security evidence while keeping separate assessments, approvals and actions for each service it supports, so teams can see what is reviewed, what is outstanding and which service is affected.
A first system may prioritise consistent assessments and easier third-party participation. A replacement may also need group reporting, local workflows and connections to existing risk and procurement systems.
How this page uses two terms
Third parties and suppliers: Your bank's service providers and other external relationships.
Software suppliers: The software companies you are considering for TPRM.
These seven factors organise the main areas to assess when choosing TPRM software for your bank. The considerations later on this page provide the detailed checks within each area.
Assessments, monitoring and follow-up, with connections between third parties, services, contracts and dependencies kept intact.
Records, approvals and evidence that support your requirements and can be maintained as they change.
Service providers can respond, submit evidence and handle follow-up securely, with manageable effort.
Languages and local workflows for internal teams and third parties, alongside group oversight.
Hosting, data location, access, security and recovery that meet your bank's requirements.
Connections to procurement and risk systems, and credible plans for later risk functions.
A supplier or partner that can deliver and support the setup in your bank's markets.
For the detailed checks within each factor, continue to the key considerations further down the page.
A bank operating in several Asian markets rarely works in one language, under one regulator or with one way of approving work. Those differences reach the software too: what your teams and service providers need to see, where the system's data should reside, and where implementation and support come from. Many software suppliers have few offices in Asia, so implementation may be done remotely, support may come from another region and time zone, and the system and its data may be hosted in only a few countries in Asia. Those hosting options may not meet your internal policy or regulatory needs.
Languages and local workflows
Markets may need different questionnaires, approval routes and languages, for your teams and for your service providers.
Hosting and regional coverage
A supplier may sell across Asia but host in only a few countries, with support based elsewhere or through local partners.
Remote or on-site delivery
Some suppliers implement by video call. If you need on-site help with design, testing or training, confirm who provides it.
These eight suppliers are examples, not a shortlist. There are many more TPRM suppliers in the market. These are listed alphabetically to show how suppliers differ on hosting, local presence and delivery.
Archer
Third-Party Risk Management
Covers the third-party lifecycle from onboarding and assessment through to termination, with configurable questionnaires and automated scoring.
Vendor portal
A dedicated interface for service providers to answer questionnaires and upload SOC and PCI evidence.
Fourth-party mapping
Tracks the dependencies behind your providers, so a shared upstream supplier becomes visible.
Issue management and remediation
Records gaps found during assessments and tracks the provider's remediation through to closure.
Check before shortlisting
External users typically complete assessments through the Archer Engage portal, which can add licensing and configuration work compared with lighter platforms. Ask to see the invitation-to-submission process, and confirm which partner would deliver this in your countries.
Diligent
Third-Party Manager
Covers onboarding, screening and continuous monitoring, with due diligence depth set by the risk tier you assign.
Ownership mapping
Traces complex ownership structures to identify the ultimate beneficial owners behind a provider.
Continuous screening
Alerts on sanctions, watchlist and politically exposed person matches across the provider network as they arise.
Risk-tiered due diligence
Segment providers by tier and apply a different depth of checking to each.
Check before shortlisting
Its strength is screening and intelligence rather than questionnaire workflow, and reviews note the portal your providers use is less straightforward than lighter platforms. Ask to see a provider complete an assessment end to end.
Fusion Risk Management
Third-Party Risk Management
Approaches third-party risk from the service the provider supports, mapping each one to the business processes and systems that depend on it.
Dependency mapping
Links providers to specific banking processes and IT systems, so the effect of an outage is visible before it happens.
Fourth-party insights
Identifies the providers behind your providers to expose concentration in the supply chain.
Continuous monitoring
Connects to external data providers for alerts on security posture and financial health.
Check before shortlisting
Confirm where implementation and support would be delivered from for your countries, and whether a local partner is involved. Building the dependency maps is also where most of the setup effort goes.
MetricStream
Third-Party Risk Management
Covers onboarding, assessment and ongoing monitoring, with tiering driven by how important a provider is and what data it can reach.
Third-party portal
A dedicated interface for providers to submit assessments, certifications and due diligence documents.
Risk-based tiering
Sorts providers into tiers automatically, based on access to sensitive data and importance to operations.
Fourth-party tracking
Extends visibility beyond direct providers to find concentration further up the chain.
Check before shortlisting
Implementation typically needs real internal IT or consulting effort because of the platform's depth, so agree who does that work and over what period before committing.
OneTrust
OneTrust Third-Party Management
Covers screening, tiering, assessment and monitoring, with external cyber ratings available alongside your own assessments.
Automated tiering
Sets inherent risk from the intake survey, which then governs how deep the assessment goes.
Assessment extraction
Reads documentation a provider supplies and drafts questionnaire answers from it for review.
Issues management
Assigns remediation tasks to both your internal owners and the provider's own team.
Check before shortlisting
Its cyber ratings come from external exchanges, and the supplier itself notes these can produce false positives or lag real events, so decide what you would do with a rating before relying on one. Only two APAC offices are recorded, so confirm who would implement and support you locally.
Protecht
Vendor Risk Management
Covers the third-party lifecycle from due diligence through monitoring to contract renewal, with scoring that combines questionnaire answers and external intelligence.
Vendor portal
A dedicated interface for providers to complete questionnaires and upload compliance documents.
Criticality-based tiering
Assigns tiers from the data a provider can reach and its importance to core services.
Fourth-party visualisation
Maps dependencies on sub-providers to show where concentration builds up.
Check before shortlisting
It is a connected vendor-risk workflow rather than a cyber-rating product, so if you want external security ratings, confirm which intelligence provider it would connect to and what that costs. Its only recorded regional office is in Australia, so establish who would implement and support you in your own country.
Riskonnect
Third-Party Risk Management
Covers the third-party relationship from first assessment through to ongoing monitoring, with dependency mapping tying providers to the processes they support.
Dependency mapping
Connects providers to the critical business processes that rely on them, for resilience planning.
Continuous monitoring
External feeds give ongoing updates on provider financial and cyber health between assessments.
Assisted intake
Screens and categorises a provider from intake data to set the assessment path.
Check before shortlisting
Reviews note the volume of assessment templates can overwhelm a small team, so check how much tailoring the standard set needs before your providers see it. Delivery and support teams in the region are spread across several countries, so confirm which one would serve your bank.
ServiceNow
Third-Party Risk Management
Covers assessment and ongoing monitoring of providers, and can trigger a risk assessment straight from a procurement or sourcing request if your bank already runs ServiceNow.
Vendor assessment portal
A dedicated workspace where providers complete questionnaires, upload evidence and track their remediation tasks.
Questionnaire workflow automation
Handles distribution, reminders and escalation when responses run late.
Automated risk tiering
Sets the tier from service criticality and initial screening data.
Check before shortlisting
The supplier notes that banks managing very large provider populations may see slower response when running platform-wide cross-referencing. Delivery runs through an implementation partner, so confirm which partner covers your countries and its experience with this product in a bank.
* Self-hosted deployment may be available through a separate arrangement rather than the standard cloud subscription.
For certainty, confirm any critical points in the supplier details above directly with the supplier.
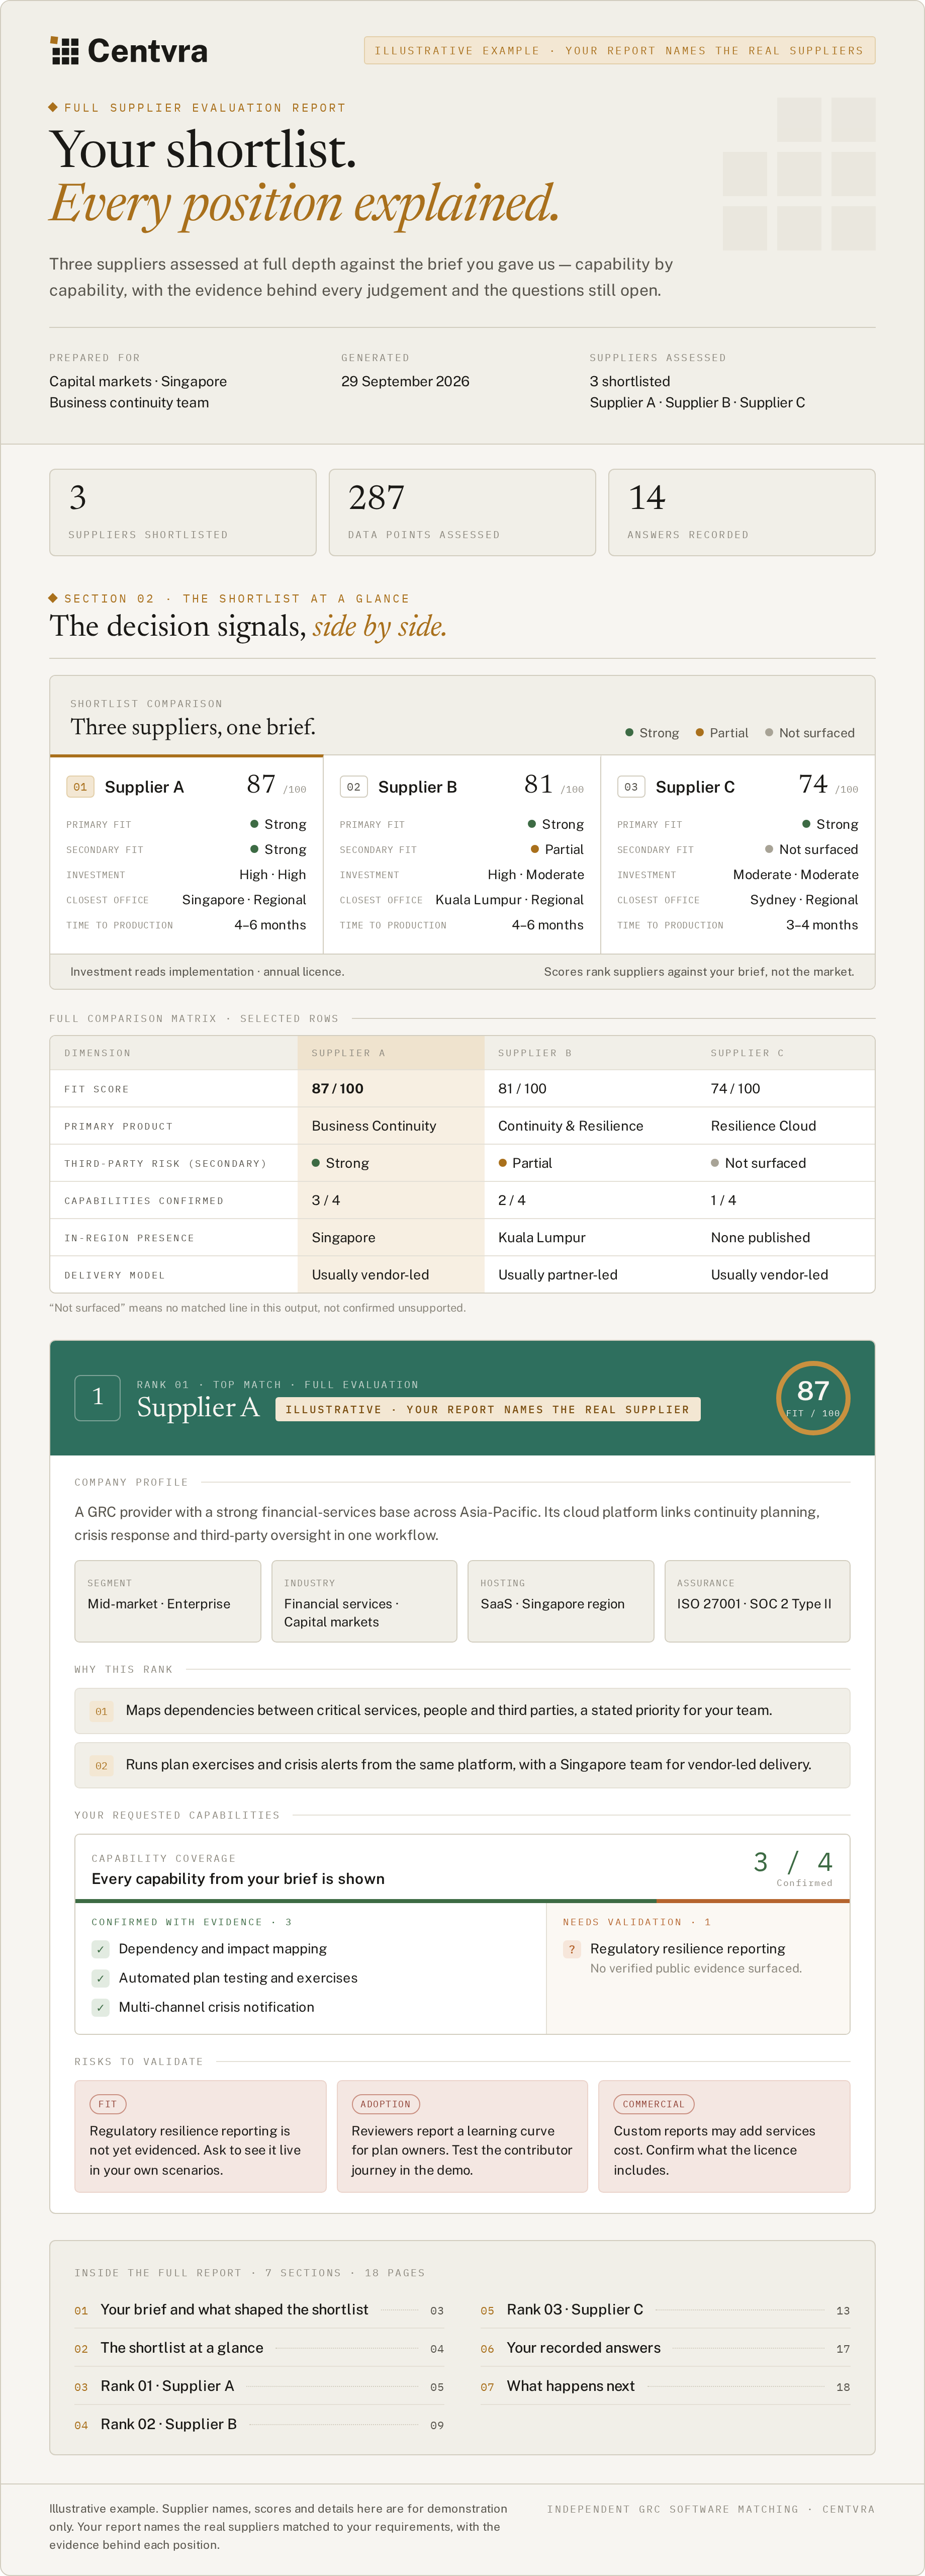
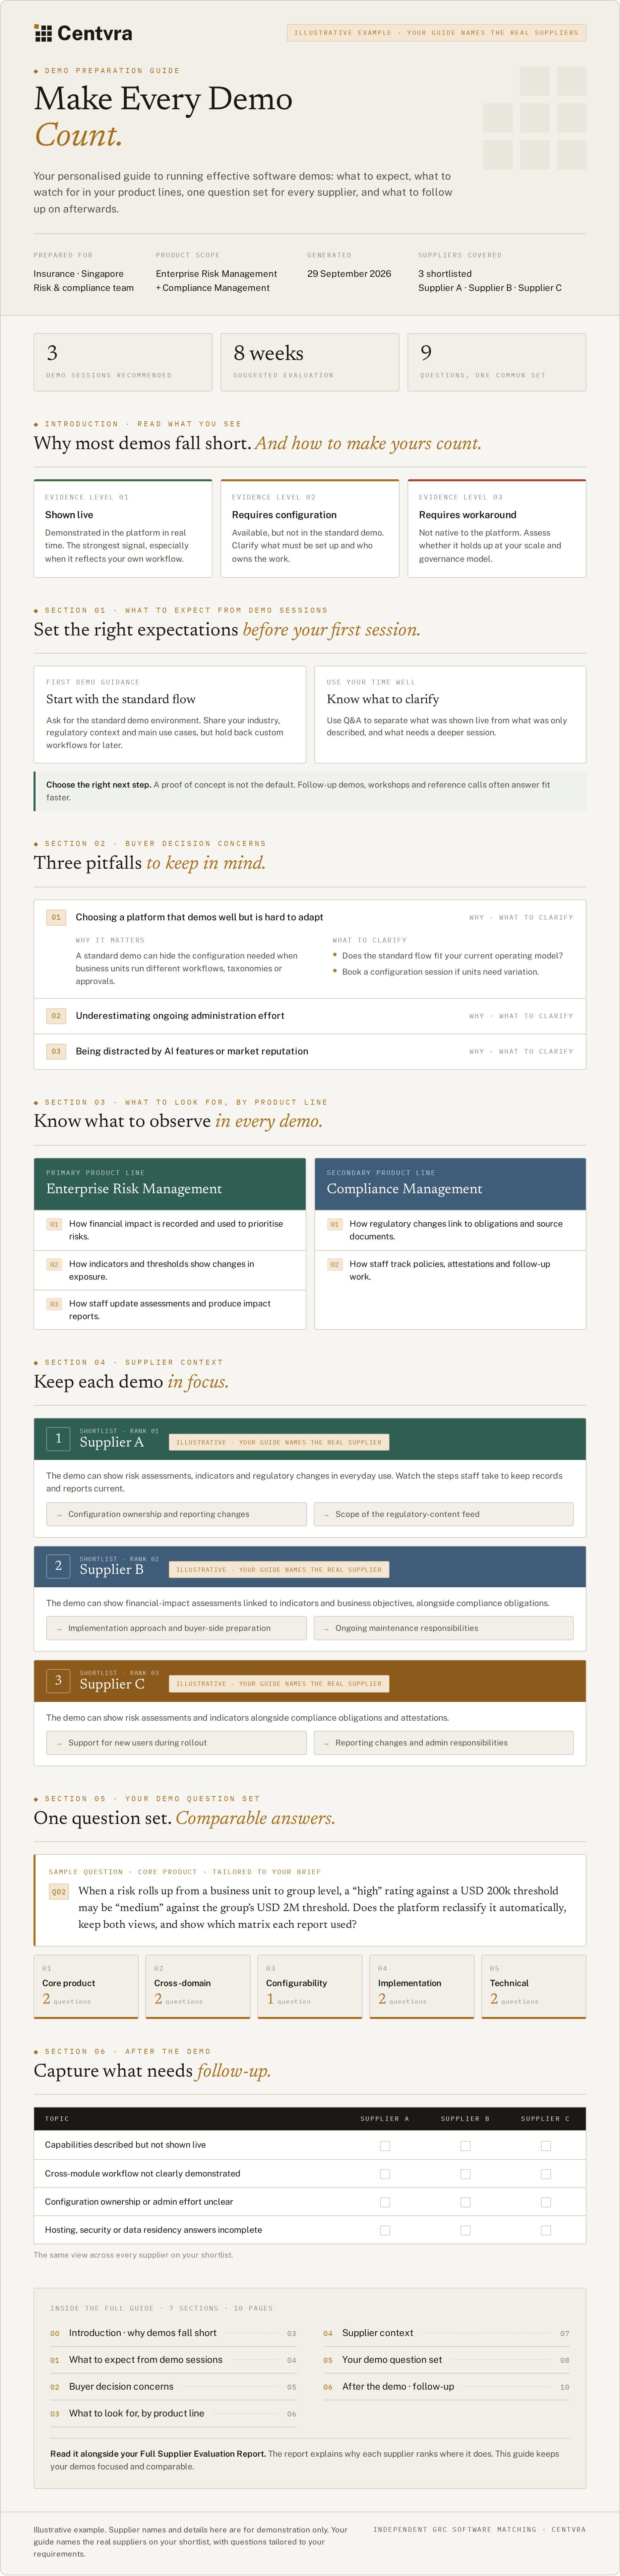
Centvra matching
Research every supplier yourself, or start from a shortlist you can justify.
Describe your requirements in a sentence or two. Centvra reads your context and prepares a curated set of questions tailored to your bank. It then scores each supplier in our catalogue against your answers with Centvra's proprietary scoring model, built specifically for GRC software selection, and explains why each one on your shortlist fits, so you can show how the shortlist was reached.
With your shortlist, you can also receive these. Click one to preview it.
Almost every TPRM platform covers the basics: sending questionnaires, collecting evidence and recording reviews. Those features rarely separate one supplier from another. The six capabilities below are where products differ most, and where a supplier's answer is most worth checking.
Fourth-party mapping
Records the subcontractors and cloud providers behind each service provider, so you can see when several of them depend on the same upstream company. Ask how fourth-party details are collected, and how often they are kept up to date.
Your own risk scoring
Lets your team build the scoring model, weight the factors that matter to your bank, and have the system assign each provider or service to a risk tier. Check whether you can change the model yourselves, without paying the supplier.
Continuous monitoring
Brings cyber ratings, financial health, sanctions and adverse news onto the provider record between formal reviews, and alerts you when something changes. Ask which data feeds are included, and how well they cover providers in Asia.
Evidence review
Uses AI to read questionnaire answers, policies and audit reports, and flag gaps or answers the evidence does not support. Your team still makes the decision. Ask whether documents are sent to an outside AI service.
Obligation tracking
Tracks each provider's contractual and regulatory obligations, such as breach notice deadlines, data residency and cross-border transfer rules, and flags when one is due or missed. Check that it can hold the rules for each country you operate in.
Contract clause extraction
Uses AI to read contracts and pull out audit rights, breach notice, renewal and exit terms, so reviewers do not read every page. Check its accuracy on contracts in your languages, and where they are processed.
Ask the supplier
One service provider may support several banking services under different contracts. The bank may use one provider-level questionnaire to collect financial audit reports or environmental, social and governance (ESG) information, and separate questionnaires for individual services, such as IT services or call-centre operations.
Check whether the platform can apply a provider-level questionnaire across relevant arrangements while maintaining separate service- or contract-level questionnaires, findings and risk conclusions.
For a broader comparison, see TPRM Software Capabilities: How Suppliers Actually Differ.
The bank may assess the same third party for operational, technology, cyber, privacy and financial risks. Each assessment may need different evidence, scoring and review frequencies. Shared evidence can reduce repeated requests, while each assessment retains its own scope, review date and conclusion.
Check the depth supported for each required assessment. Verify how evidence is reused and whether updated or expired evidence flags the assessments that depend on it, while preserving the basis of previous decisions.
Some TPRM software suppliers offer external intelligence through their own services or partnerships. Banks may also hold separate subscriptions to intelligence providers and need that information integrated into TPRM. Sources may cover financial information, cybersecurity findings and adverse news about third parties.
Understand how the information enters the platform and triggers alerts against the bank's thresholds or rules. Coverage can vary by country, organisation size and risk type.
Check coverage across the locations of the bank's third parties and service delivery, such as an India-based call centre supporting an ASEAN bank. Verify update frequency and support for existing intelligence subscriptions. Establish how data is linked to relevant third parties, thresholds are configured and alerts lead to investigation and tracked follow-up.
A banking group may use the same service provider across several countries or entities. Group reporting should bring these exposures together while preserving the assessments, findings and actions for each arrangement. A favourable overall rating should not obscure a serious issue affecting one critical service.
Check that consolidated reports allow teams to trace a significant issue to the affected service, assessment and follow-up action. Overdue reviews, incomplete assessments and outdated evidence should remain visible.
Assess whether the platform can support the requirements applicable to the bank's entities, countries and third-party arrangements. Relevant needs may include register information, assessments, approvals, review history, reporting and evidence of follow-up.
Example: Regulation-Driven Reassessment
Our research on Indonesia's IT service-provider framework, including PADK OJK 1/2026, illustrates how a material change such as provider ownership can create a reassessment need. Supporting software should connect the change to affected arrangements, preserve earlier assessments and record the resulting review and decisions.
Verify which applicable requirements the proposed solution supports as standard, through configuration or through additional components. Examine the records, workflows and outputs needed for specific regulatory triggers, rather than relying on a general claim of regulatory support.
Service providers may need several people to complete questionnaires, provide evidence and respond to follow-up requests. Portal participation can involve invitations, account registration and approval of additional contacts. Assess how these steps would work for the bank's service providers.
Ask the software supplier to demonstrate the process from invitation to submission, including adding colleagues, delegating work and controlling who can view or submit responses. Check external sign-in, account recovery, contact replacement and access removal when people leave.
Your bank may use the software primarily in English while sending questionnaires in Thai, Chinese or another language. Check that the system displays the questionnaires correctly and allows responses in the required language.
A regional or global rollout may also need shared group standards alongside local assessments, permissions and approval routes. Interface languages and support-team languages are separate requirements.
Ask the software supplier about any limitations when entering, displaying or exporting text in the languages your bank requires. Where available, ask to see an existing multilingual questionnaire and response in its demonstration system, including reports or exports. Check how local workflow variations and phased rollout preserve group visibility.
Confirm internally whether on-premises hosting, where the software runs on the bank's own servers, is mandatory or preferred. If cloud hosting is being considered, establish the internal clearance needed.
On-premises options are more limited. If this is mandatory, identify software suppliers that support it. Confirm that the required capabilities, integrations, external intelligence connections and third-party portal are available in the proposed deployment.
Your bank may require certain information to remain within the country where it operates. TPRM software may hold confidential contracts, assessment findings and supporting evidence. Confirm internally where this information can be stored and processed, and whether access from overseas is permitted.
Hosting in a country does not necessarily mean all information remains there. Backups, support access, connected services and artificial intelligence features may involve other locations.
Ask the software supplier to identify the countries where records and attachments are stored, processed, backed up and accessed. Compare the proposed data flows with the bank's applicable restrictions.
The TPRM platform may hold confidential findings about weaknesses in the bank's service providers. A software outage could interrupt assessments, evidence submissions and access to information needed for oversight or incident response.
Ask the software supplier for evidence of access controls, sign-in arrangements, audit history, independent security assurance and tested recovery. Confirm service-availability and recovery commitments, including recovery of records and attachments.
Implementation may be delivered by the software supplier, an implementation partner or a combination of both.
Confirm delivery arrangements for the bank's countries, including which meetings and activities will be remote or on-site. Assess the proposed team's experience with the specific software and comparable TPRM implementations. For partner-led delivery, establish how specialist software supplier support is available. Assess the implementation partner separately, including the services contract.
Business-hours support may follow the software supplier's headquarters time zone, working days and public holidays, which may differ from those of the bank and its portal users.
Confirm the support time zone, working days, holiday calendar, response commitments and escalation arrangements, including help with third-party portal access problems. Assess support-team languages separately from the languages supported by the software.
A software supplier's banking customer list does not establish the experience of the team proposed for your project. Relevant experience should cover TPRM assessments, workflows and rollout arrangements comparable to the bank's needs.
Examine relevant references and the experience and availability of the proposed software supplier or partner team. Confirm specialist oversight, escalation arrangements and how delivery quality will be maintained if the proposed personnel change.
Fit-based software matching
Tell us what the software must support, how your teams work and which delivery constraints matter. Centvra uses those inputs to build a focused supplier shortlist.
Your operating brief
Fit-based shortlist
Describe your bank's TPRM needs, operating countries and confirmed hosting or implementation requirements. Centvra identifies relevant software suppliers and explains their potential fit.
A platform may meet your bank's functional needs yet be unsuitable because of hosting restrictions, language limitations or implementation and support arrangements. Any of these can become a roadblock to selection.
This page explains the factors and considerations, helping you identify software suppliers that can support both the TPRM work and the bank's operating requirements.
It greatly narrows the available options because fewer software suppliers support deployment on the bank's own servers. Establish which products offer it, then check that the required capabilities, integrations and third-party portal are supported in that deployment.
Evaluate TPRM in depth against the bank's immediate needs, including questionnaires, assessments, evidence collection, monitoring and follow-up actions.
Use a separate, focused session with the software supplier to understand how later functions would connect with TPRM. For example, could a service provider's failed business continuity tabletop exercise be linked to its TPRM assessment and tracked through remediation?
Establish whether these connections use shared records, configuration or integration, and whether later phases would require substantial changes to the initial TPRM setup. Distinguish capabilities available today from planned developments.
There is no single answer. Local regulatory requirements, the information held in the platform and the bank's internal policies determine whether shared hosting is acceptable or certain information needs to remain in-country.
One approach is "global template, local data": the bank uses common questionnaires, assessment methods and workflows across countries, while keeping information locally where required. Information permitted to be shared is then brought together for group reporting.
Ask the software supplier whether it supports this arrangement, which hosting locations are available and how reporting works across separate deployments. Establish which records and attachments remain local, what information is shared and whether consolidated reporting requires additional integration.